 4:50:19 AM FRIDAY NOVEMBER 20, 2026
THE HACKER NEWS

cybermango
11 hours ago
Pancreatic cancer halted by virus injection in three patients
A cancer-killing virus has stopped pancreatic tumours from growing and spreading in three people in an initial safety trial, raising hopes that it may help to beat the deadly condition...

4 HOURS AGO
SP_FROM_DB
Postgres 19 is out, and it's available on Neon and Databricks Lakebase
17 HOURS AGO
NOTMINE1337
Someone reported java4shell bug in September 2026
2 DAYS AGO
ONENAME
IRA Velinsky, industrial designer for Commodore and Atari
3 DAYS AGO
RBANFFY
Talking Venice with Mahesh Subramony at AMD In-Depth
12 HOURS AGO
TERRETTA
UK government forced to admit it issued Apple a secret encryption order
16 HOURS AGO
KRTHR
Making 8-page foldable zines from a single A4 sheet in the browser
18 HOURS AGO
LIOTIER
How the European Commission rolled out Matrix to more than 40k staff
20 HOURS AGO
GHOSTFOXGOD
Distributed, high-performance blob storage on SQLite
14 HOURS AGO
TEJOHNSO
Everything you need to survive and rebuild society
2 DAYS AGO
SPEEDPING
Unauthenticated remote code execution in Nginx
A DAY AGO
YIGITDEMIRAG
Gemini 4 Neon
2 DAYS AGO
SPEEDPING
Unauthenticated remote code execution in Nginx
20 HOURS AGO
ILLIDAN1000
SSD prices may begin to decline in the latter half of 2027

hn-aarvin
5 hours ago
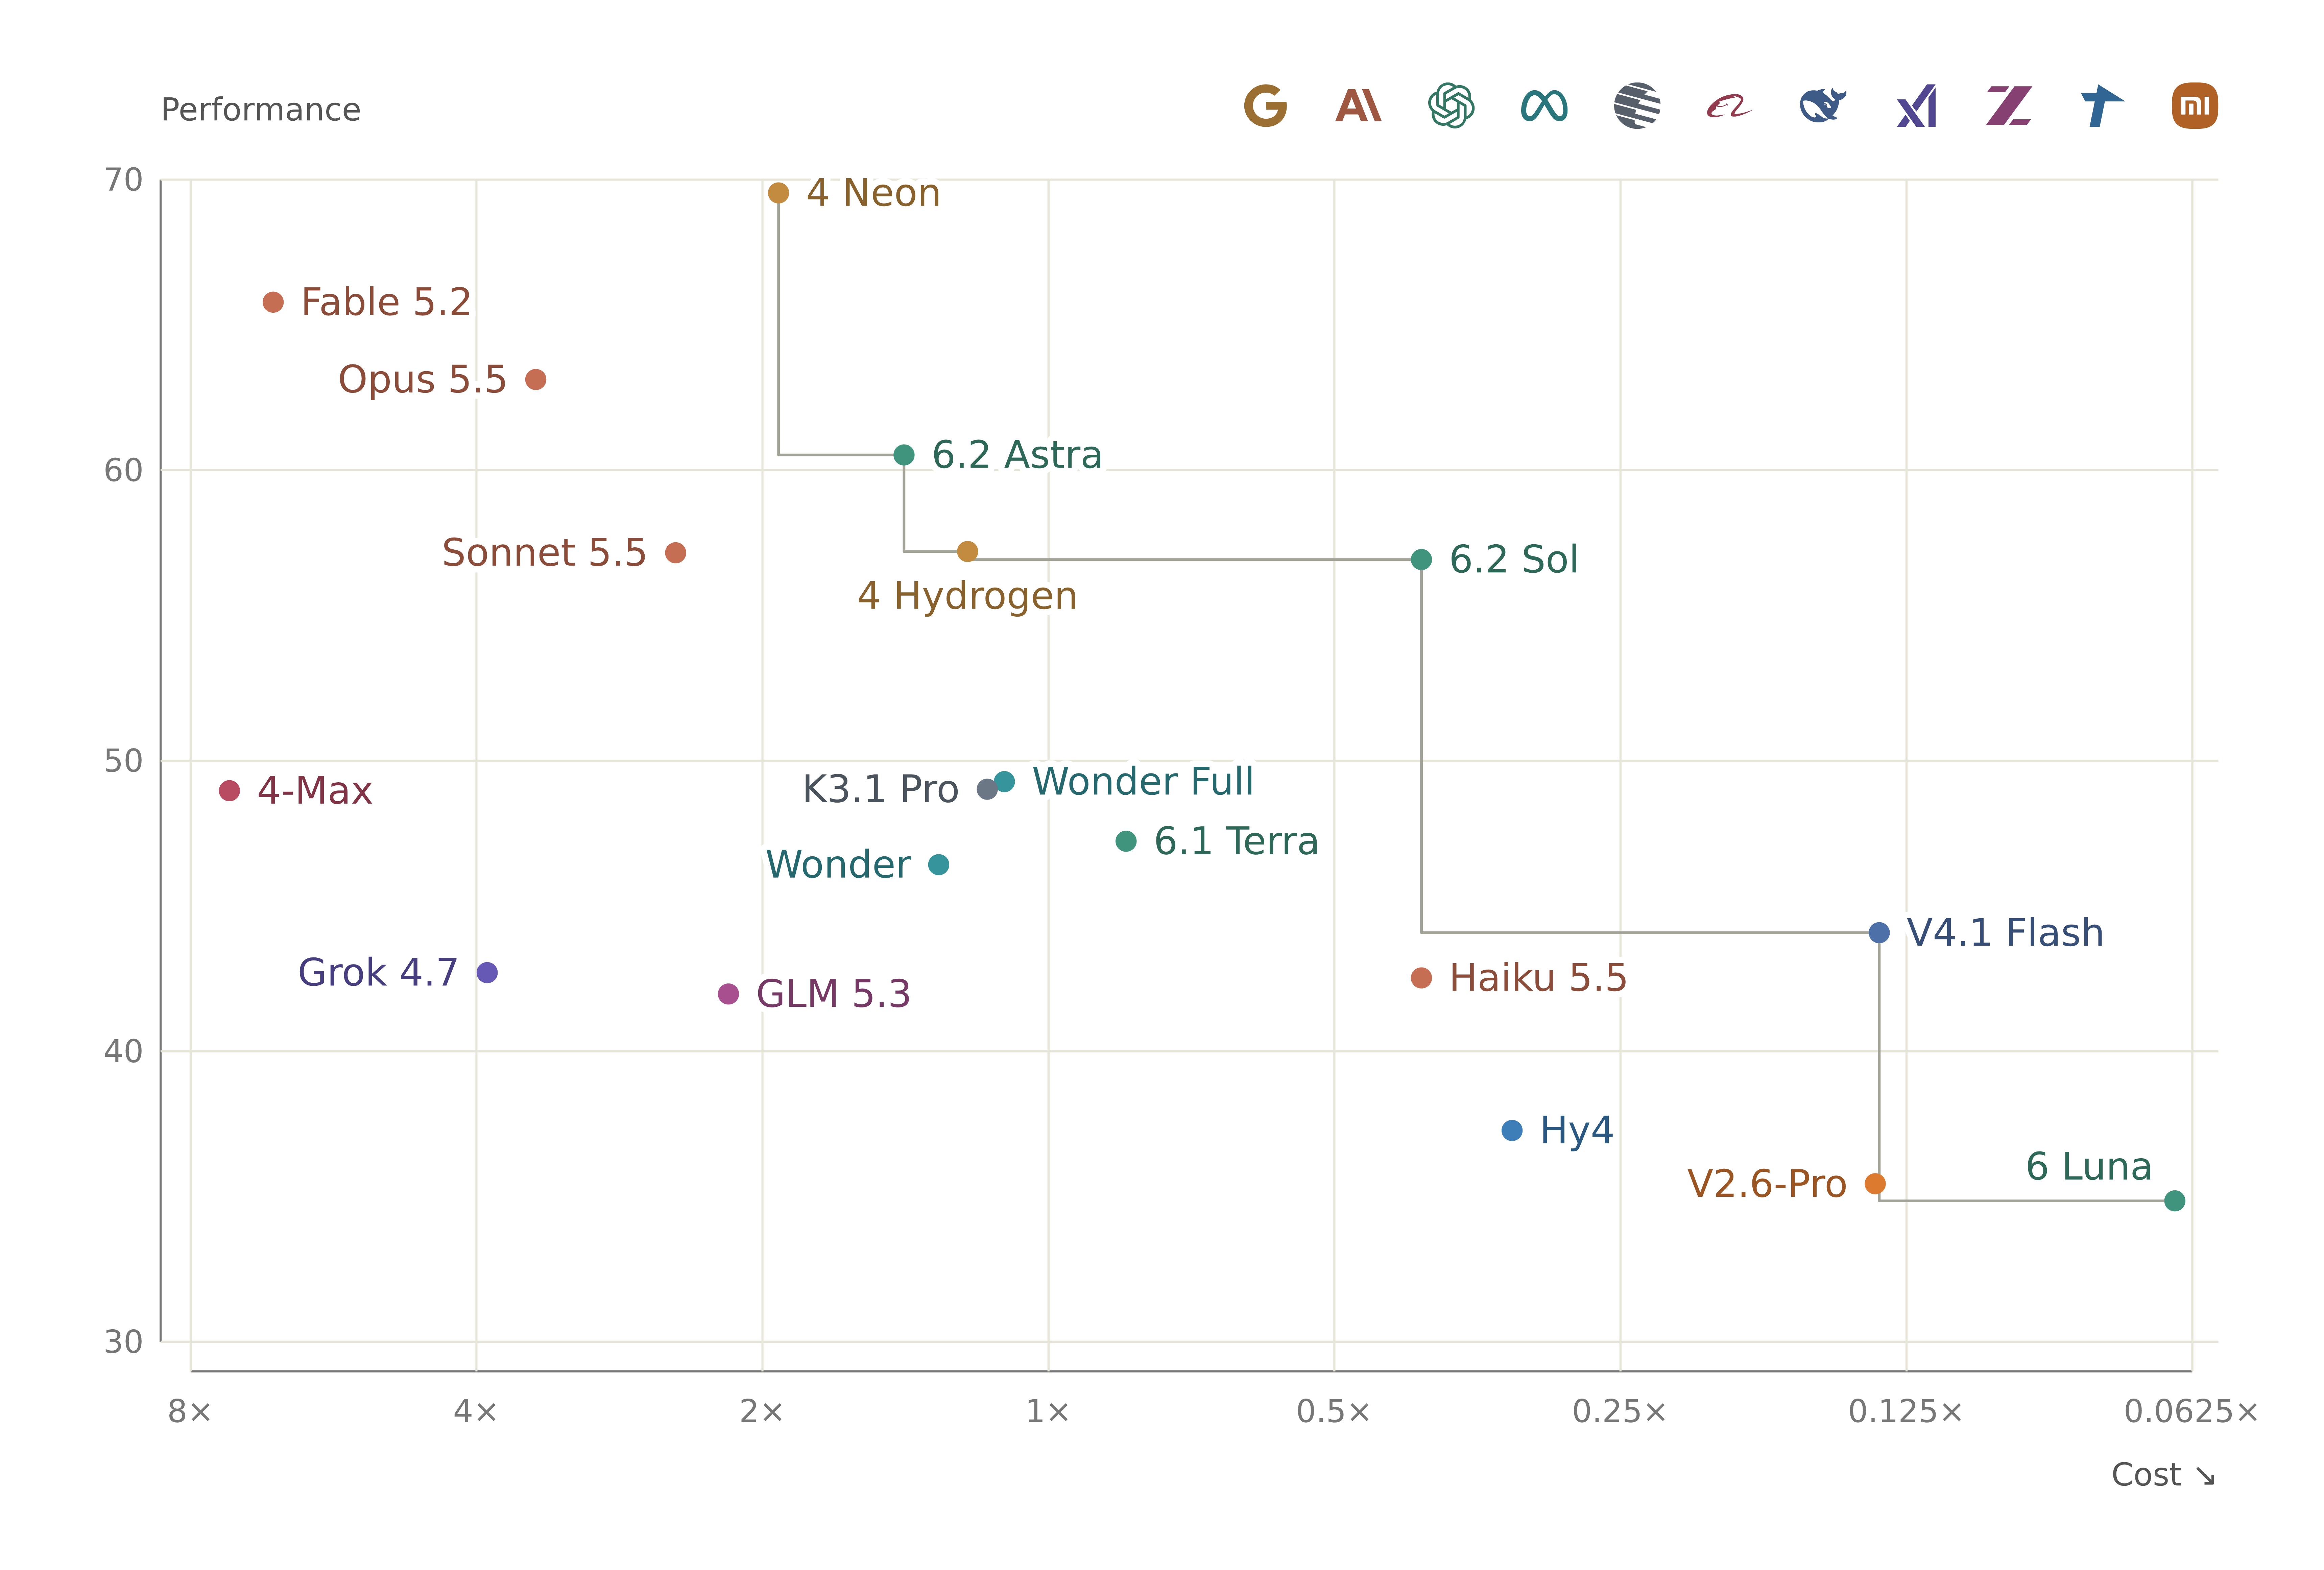
Gemini 4 Neon is the new #1 on the Models Engineering Index
Mei calculates language models' practical performance on engineering tasks.
emot
4 hours ago
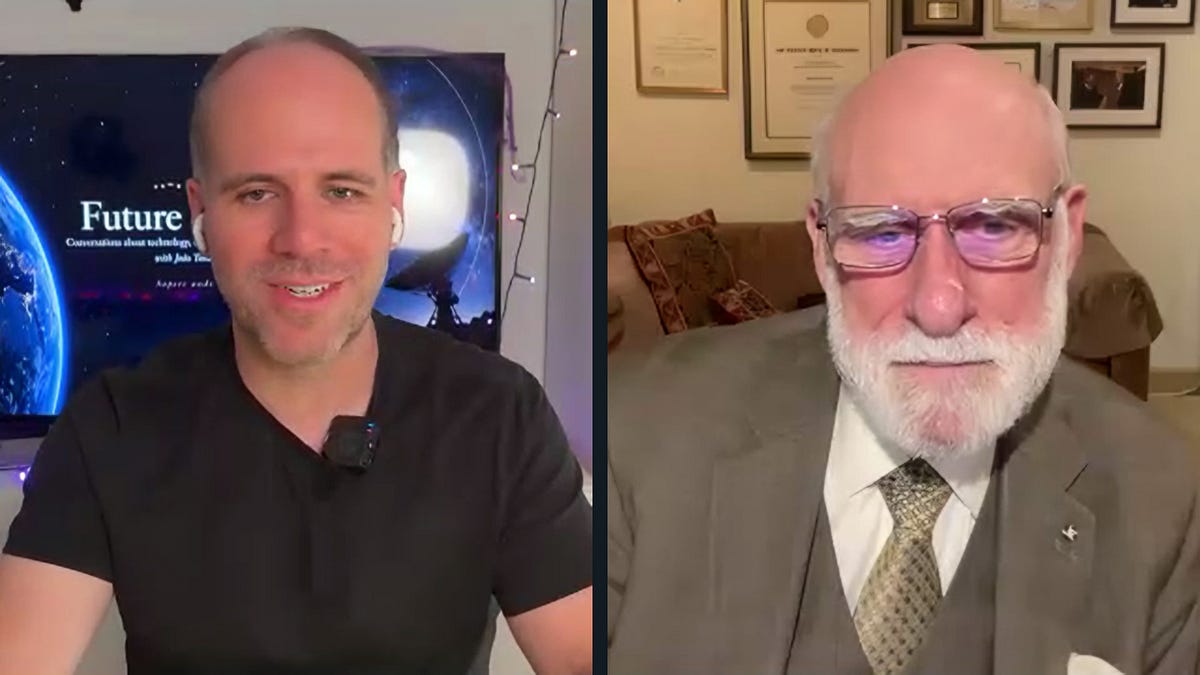
Vint Cerf on why TCP/IP was never patented
Future Stories, my new podcast about technology, science and the way we live, starts today. The first guest is one of the people who built the Internet....
harrisonpage
4 days ago
Garage Door Spam
In the beginning, my garage door opener worked fine. When the door opened or closed, I would get a notification. If I'm away from home and the door opens, so......


dev1one1
10 hours ago
The 98% Slot Machine: How Paid Advertising Became an Extraction Tax
Ad auctions are calibrated to pay out just enough to keep you playing. The winners of the auction don't win profits; they win the privilege of working for free as unpaid fulfillment contract...
cybermango
11 hours ago
Claude solves two open problems in the physics of black holes
Claude Fable 5.2 has solved two open problems in theoretical physics. Both concern black holes and the search for a theory of quantum gravity....
o4c
3 days ago
How to CAD Almost Anything
Have you ever wondered how objects from our daily lives are designed? How can we generate a computer 3D model of a mug, a bottle of Diet Coke, or a Saturn V rocket? What about designing the ...

qtqtqt
an hour ago
GIMP now has UI tests
GIMP now has automatic tests that use the user interface in the same way as a person....
JacobHenner
3 hours ago
OpenSSL: Buffer overflow in EVP_EncodeBlock() (CVE-2026-121481, CVSS 9.8)
This fixes "Buffer overflow in EVP_EncodeBlock()" (CVE-2026-121481) by returning -1 for invalid inputs to EVP_EncodeBlock(): NULL input or output buffers, negative lengths, and len...
lexandstuff
2 days ago
Weight-Space Programming builds neural networks like a 1990s researcher
The writing aspect of WSP turns out to be quite a history lesson....
choult
7 hours ago
Synology Security Advisory
Synology Product Security Advisory...
cornholemedia
13 hours ago
Show HN: Cornhole News – A Hacker News inspired site for news across the Midwest
Top stories and links, ranked by votes from the community....
g0xA52A2A
2 days ago
Automatic Checking of Compiler Correctness with E-Graphs
A tricky domain for automated theorem proving...
todsacerdoti
8 hours ago
Rebuilding my local voice assistant pipeline
Swapping openwakeword for microwakeword and making voice detection smarter...
evan_
4 hours ago
ChatGPT for SNES
An unofficial experiment: a small language model running on the Super FX chip of a Super NES cartridge. Not made or endorsed by OpenAI....
tison
4 days ago
Reverse-Engineering Kevin J. Lang's Lost OCaml Code in Apache DataSketches
Another feat from Gemini 4 Carbon Orchestrator + Swarm: reconstructing the magic lookup table generators behind CpcSketch in Apache DataSketches.
It all started six months ago, when I spotte...
datascientist
13 hours ago
Pete warden on local AI, open models, voice interfaces, the future of hardware
Pete Warden on Local AI, Open Models, Voice Interfaces, and the Future of Hardware. Subscribe: Apple • Spotify • Overcast … More...